



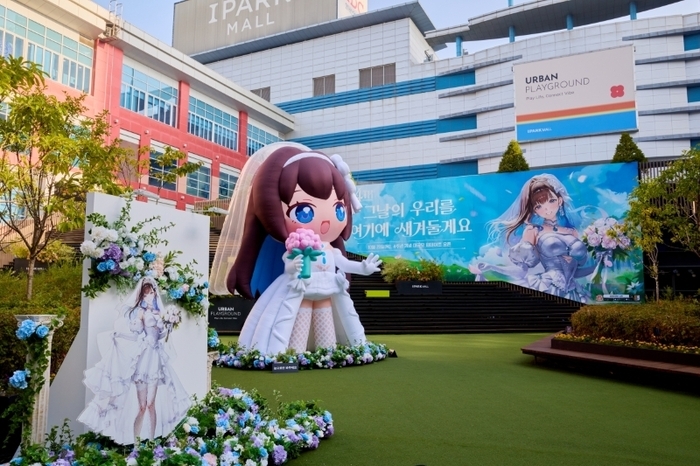
A security analysis report published on GitHub on the 4th revealed that four JavaScript files in Level Infinite's Content Delivery Network (CDN), called by the PC launcher of *Victory Goddess: Nike* (developed by ShiftUp), showed signs of tampering that invoked external malware.
The files were modified on September 27 and could have allowed remote control programs to run on some PCs since at least October 23.
The attack involved the official launcher fetching tampered CDN files, which then downloaded additional programs from external servers. Experts assessed this as a supply chain attack, caused by insufficient security verification for malicious packages inserted during the software development and distribution process.
The analyzed program could execute arbitrary commands, access/download files, and capture screens. It could also target passwords and cookies stored in web browsers, developer tool authentication data, and virtual asset wallet information. However, the actual scale of personal data breaches or infected users remains unconfirmed.
The *Nike* operators stated, “We identified an anomaly suggesting the PC launcher's script files may have been tampered with by a third party,” and added, “We proceeded with client fixes and updates around 2:30 AM today.” They are currently investigating the scope of impact and reviewing additional measures.
The concern lies in the scale of Level Infinite's CDN services. As a global gaming brand under Tencent, Level Infinite provides services for major titles like *PUBG Mobile* and *Mobile Legends: Bang Bang*, alongside *Nike*. *PUBG Mobile* has surpassed 1 billion global downloads, while *Mobile Legends: Bang Bang* boasts over 100 million daily users. Overseas communities speculate the issue might have spread to other Level Infinite/Tencent games, including *Delta Force*.
The repercussions will depend on whether this was an isolated incident affecting only *Nike* or a breach of Level Infinite's shared CDN or internal distribution system. In global publishing environments where infrastructure is shared across countries and game services, a security breach in one area could cross borders and impact users worldwide.
Kim Jae-gi, Chief Product Officer (CPO) of S2W, emphasized, “To prevent supply chain attacks, security must be verified at every stage—not just the development code but also packages used in the build process. A procedure to check for vulnerabilities and malware throughout the entire software lifecycle, from development to distribution, is essential.”
